 Security · 7 min read
Add HTTP Security Headers: CSP, nosniff, Referrer-Policy and More
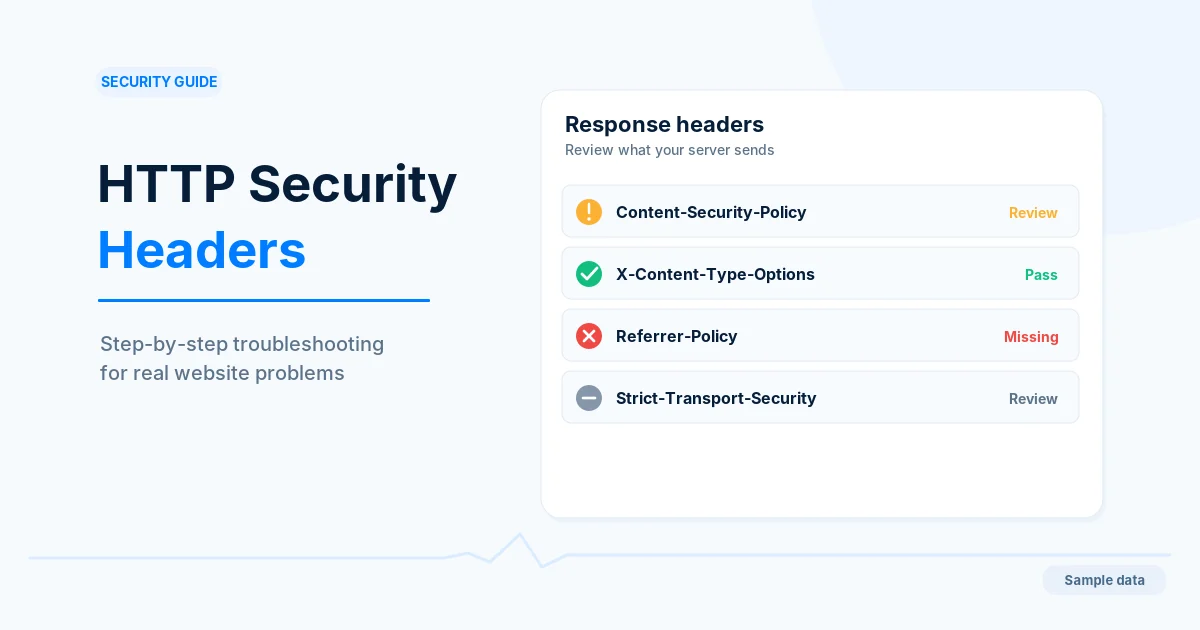
Add the common browser security headers safely: Content-Security-Policy in report-only first, nosniff, framing, Referrer-Policy and Permissions-Policy.
Practical, step-by-step website launch and SEO health guides.
Showing 1 to 9 of 9 guides in Security
Security · 7 min read
Add the common browser security headers safely: Content-Security-Policy in report-only first, nosniff, framing, Referrer-Policy and Permissions-Policy.
Security · 7 min read
Review the Cloudflare settings that affect crawling: SSL mode, bot protection, Under Attack mode, Rocket Loader and managed robots.txt.
Security · 7 min read
Find images, scripts and styles loaded over http:// on HTTPS pages, fix them at the source and confirm the browser warnings are gone.
Security · 10 min read
Spot injected spam pages and links on a hacked site, contain the breach, clean and harden it, then ask Google to review the fix in Search Console.
Security · 11 min read
Add the Strict-Transport-Security header in stages, from a five-minute max-age to one year, and decide whether the HSTS preload list is right for you.
Security · 9 min read
Install a certificate, fix mixed content, add canonicals and 301 redirects, update Search Console and sitemaps, then add HSTS once everything works.
Security · 8 min read
Read the Search Console security issues report, safely confirm hacked content or malware, clean the site, close the cause and request a security review.
Security · 11 min read
Find out why a browser or crawler rejects your HTTPS certificate, test expiry, hostname and chain with OpenSSL, and fix it without breaking redirects.
Security · 9 min read
Build a content security policy in report-only mode, fix what it flags, then enforce it with nonces or hashes so scripts and styles keep working.